
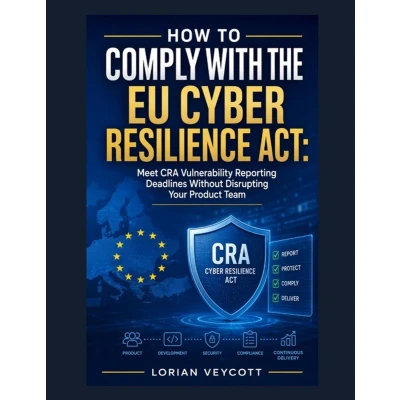
How to Comply with the EU Cyber Resilience Act: Meet CRA Vulnerability Reporting Deadlines Without Disrupting Your Product Team
Uitgelicht

|
18,77 |
Naar shop
|

|
18,77 |
Naar shop
|
|
19,00 |
Naar shop
|
| VERGELIJK ALLE AANBIEDERS (3) | ||
 Beschrijving
Bol
Your product ships to the EU. Starting September 2026, a vulnerability report clock starts ticking the moment your team learns of active exploitation - 24 hours for an early warning, 72 for full notification, 14 days for a final report after a fix ships. Most CRA guidance stays theoretical: definitions, mappings, legal summaries nobody on your engineering team will actually read. This book is different. It's a practical build plan that turns Article 14 into working infrastructure - an automated SBOM, a detection pipeline, a response team with real authority, a rehearsed three-stage reporting process, and a pipeline where compliance runs natively instead of sitting bolted on top as a separate burden. By the end of this book, you will be able to: - Determine whether your product falls in scope of the CRA and identify its risk classification - Build a working SBOM pipeline that answers "are we affected" within minutes, not days - Design an internal escalation path that meets the 24-hour early-warning deadline - Draft a Coordinated Vulnerability Disclosure policy your engineering team will actually follow - Register for and navigate the ENISA Single Reporting Platform once operational - Assign clear ownership for vulnerability triage without waiting on legal sign-off inside the reporting window - Distinguish CRA obligations from overlapping NIS2 and DORA duties to avoid duplicated effort - Prepare technical documentation and audit-ready evidence for market surveillance authorities - Integrate CRA vulnerability handling into existing CI/CD and release workflows without slowing delivery >The book follows a three-stage build: first establishing scope, timeline, and ownership; then constructing the technical backbone (SBOM, detection, response team, the full reporting sequence); then hardening that backbone into pipeline-native infrastructure that survives staff turnover, regulatory overlap, and the years of ordinary operation that follow the first deadline. This book is for product managers, engineering leads, security leads, and compliance officers at software and hardware companies selling into the EU who need CRA vulnerability reporting standing up before the deadline arrives. Stop treating this as a legal problem waiting on outside counsel. Start building the infrastructure your team can actually run.


 Beschrijving
(1)
Your product ships to the EU. Starting September 2026, a vulnerability report clock starts ticking the moment your team learns of active exploitation - 24 hours for an early warning, 72 for full notification, 14 days for a final report after a fix ships. Most CRA guidance stays theoretical: definitions, mappings, legal summaries nobody on your engineering team will actually read. This book is different. It's a practical build plan that turns Article 14 into working infrastructure - an automated SBOM, a detection pipeline, a response team with real authority, a rehearsed three-stage reporting process, and a pipeline where compliance runs natively instead of sitting bolted on top as a separate burden. By the end of this book, you will be able to: - Determine whether your product falls in scope of the CRA and identify its risk classification - Build a working SBOM pipeline that answers "are we affected" within minutes, not days - Design an internal escalation path that meets the 24-hour early-warning deadline - Draft a Coordinated Vulnerability Disclosure policy your engineering team will actually follow - Register for and navigate the ENISA Single Reporting Platform once operational - Assign clear ownership for vulnerability triage without waiting on legal sign-off inside the reporting window - Distinguish CRA obligations from overlapping NIS2 and DORA duties to avoid duplicated effort - Prepare technical documentation and audit-ready evidence for market surveillance authorities - Integrate CRA vulnerability handling into existing CI/CD and release workflows without slowing delivery >The book follows a three-stage build: first establishing scope, timeline, and ownership; then constructing the technical backbone (SBOM, detection, response team, the full reporting sequence); then hardening that backbone into pipeline-native infrastructure that survives staff turnover, regulatory overlap, and the years of ordinary operation that follow the first deadline. This book is for product managers, engineering leads, security leads, and compliance officers at software and hardware companies selling into the EU who need CRA vulnerability reporting standing up before the deadline arrives. Stop treating this as a legal problem waiting on outside counsel. Start building the infrastructure your team can actually run.
 Productspecificaties
 Prijshistorie
* Prijshistorie bevat geen data van Amazon, Amazon Marketplace.
Prijzen voor het laatst bijgewerkt op:
 Gerelateerde resultaten


