

€ 31,99 Gratis verzending

Uitgelicht
|
|
31,99 |
Naar shop
|

|
34,71 |
Naar shop
|

|
34,71 |
Naar shop
|
| VERGELIJK ALLE AANBIEDERS (3) | ||
 Beschrijving
Vergelijk aanbieders (3)
€ 31,99 Gratis verzending
€ 34,71 Gratis verzending
€ 34,71 Gratis verzending
Winkels met andere maten
Beschrijving
(1)
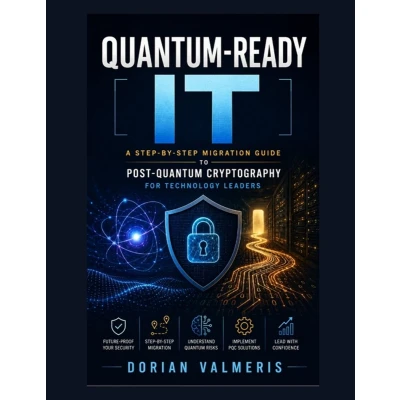
Your cryptography is hidden in more places than your risk register admits. If quantum migration starts with an algorithm debate, the program is already late. Quantum-Ready IT shows CIOs, CISOs, architects, infrastructure leaders, and risk owners how to turn post-quantum cryptography into governed IT work. Instead of abstract theory, it gives you the practical artifacts a migration program needs: exposure registers, inventory fields, prioritization models, pilot plans, vendor evidence gates, exception rules, staffing plans, board metrics, and an operating rhythm that keeps the architecture ready after the first wave. - Build an executive decision memo that creates owners and next actions - Map public key cryptography across data, trust, certificates, signing, identity, protocols, vendors, and legacy systems - Create a cryptographic inventory that teams can maintain - Rank migration priorities by data lifetime, trust impact, feasibility, and evidence quality - Apply NIST PQC standards at decision depth - Design crypto agility through control points, policy gates, tests, logs, and rollback - Plan TLS, certificate, code signing, supply chain, IAM, VPN, SSH, and internal protocol migration - Manage vendor claims with product specific evidence - Run a PQC pilot that produces rollout rules instead of theater > The method follows QRAM, Quantum-Ready Architecture Migration: inventory, prioritize, pilot, govern, report, and repeat. Each chapter turns technical risk into artifacts a leader can assign, review, fund, and defend. This book is for technology leaders who need a migration plan that can survive real systems, real vendors, real boards, and real change windows. Start before hidden cryptography turns into a business continuity surprise.
 Prijshistorie
* Prijshistorie bevat geen data van Amazon, Amazon Marketplace.
Prijzen voor het laatst bijgewerkt op:
 Gerelateerde resultaten
 Productspecificaties


