

€ 28,95 Gratis verzending

Uitgelicht
|
|
28,95 |
Naar shop
|
|
28,95 |
Naar shop
|
|
28,95 |
Naar shop
|
| VERGELIJK ALLE AANBIEDERS (3) | ||
 Beschrijving
Vergelijk aanbieders (3)
€ 28,95 Gratis verzending
€ 28,95 Gratis verzending
€ 28,95 Gratis verzending
Winkels met andere maten
Beschrijving
(1)
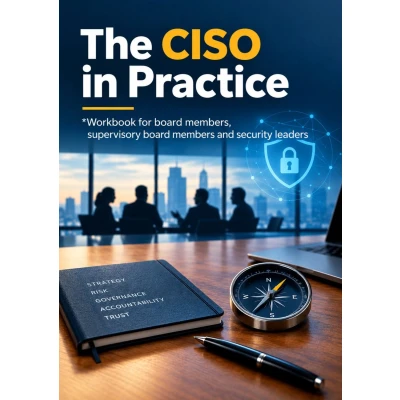
Almost every organisation now has a CISO, but what that person is allowed, required and able to do varies widely. Since the Dutch Cybersecurity Act (Cyberbeveiligingswet) and the Belgian NIS2 Act, cybersecurity is also explicitly a responsibility of the board. The CISO in Practice shows how a CISO turns that responsibility into something that can actually be carried out. The book first covers the role, the core tasks and the skills required. It then turns to governance: what the board may expect, the best position within the organisation, the mandate, building a team, tasks that do not belong with the CISO, and a salary indication for the Netherlands and Belgium. It also addresses the relationships with the CIO, CFO, DPO, audit and the business, as well as common mistakes and how to become a partner rather than a roadblock. Each chapter ends with a workbook section containing reflection questions, checklists, exercises and templates. The toolkit includes a CISO charter, a board agreement, a KPI/KRI dashboard and four 90-day plans. For board members, supervisors and (aspiring) CISOs who want to make security genuinely governable.
 Prijshistorie
* Prijshistorie bevat geen data van Amazon.
Prijzen voor het laatst bijgewerkt op:
 Gerelateerde resultaten
 Productspecificaties


