

€ 12,95 Gratis verzending

Uitgelicht
|
|
12,95 |
Naar shop
|

|
12,95 |
Naar shop
|
|
13,50 |
Naar shop
|
| VERGELIJK ALLE AANBIEDERS (3) | ||
 Beschrijving
Vergelijk aanbieders (3)
€ 12,95 Gratis verzending
€ 12,95 Gratis verzending
€ 13,50 € 2,99 verzendkosten Totaal € 16,49
Winkels met andere maten
Beschrijving
(1)
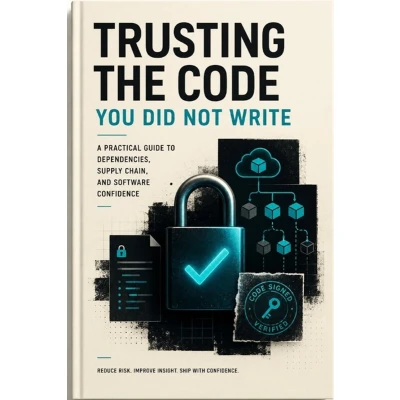
Trusting the Code You Did Not Write gives readers a structured way to understand software supply chain security without flattening the field into advice. A misleading account makes dependencies sound decisive, but the stronger reading checks it against package registries, build provenance, and code signing. The book follows a concept to evidence to system path, then turns toward safeguards, comparison, and future questions. The harder sections examine SBOM, dependency confusion, and vulnerability scanning as failure points that change the quality of a decision. Comparison points throughout the book help separate similar terms that often get blurred together. Readers finish with sharper vocabulary, stronger evaluation habits, and a clearer sense of what remains uncertain. The reader gains a vocabulary for disagreement and a method for checking evidence before acting. Readers get a field-specific way to discuss package registries, code signing, and dependency confusion without collapsing them into one idea. Examples tied to vulnerability scanning help readers notice when a confident explanation needs more context or better records.
 Prijshistorie
* Prijshistorie bevat geen data van Amazon, Amazon Marketplace.
Prijzen voor het laatst bijgewerkt op:
 Gerelateerde resultaten
 Productspecificaties


